
6.0 KiB
6.0 KiB
Anti-Virus
- Signature-based detection
- Store some small code signature for each virus
- Scan files either in bulk or at run-time, compare with the signatures on file
- Generic signatures
- Hashing the entire file is a bad idea, the author only needs to add a
nopto completely change the signature- Also hashing every executable is slow
- Instead we identify key pieces of the malware and hash that
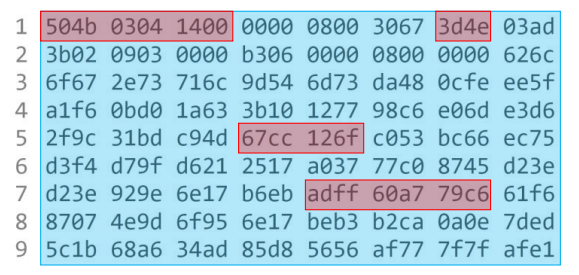
- This method is never going to catch a virus it’s never seen before
- Heuristics
- Determine what actions and rules a virus program will normally adopt
- Start the program in a
VMand see what it does - Theoretically could detect a virus that doesn’t strictly match some signature
- Only if it does the same thing as a virus its seen before
- A lot slower than signature detection as it needs to be run in a VM before the user is allowed to open it
- What if the virus sleeps for 20 seconds before doing anything? very hard to detect
- Machine learning


Network Attack Models
- Firewalls don’t protect against
- Attacks using valid protocols
- Insider attacks
Intrusion Detection Systems (IDS)
- Detects possible intrusion attempts
- Generates alerts and logs for administrators
Intrusion Prevention Systems (IPS)
- Identical to IDS except also stops the attack
IDS Deployment
- Host-based (HIDS)
- Monitors a single host to find suspicious activity including resource / app usage
- In many ways modern anti-virus does this
- Additional layer of security software running on a host within a protected LAN or VPN
- Creates a profile of usage for specific users
- Can monitor CPU, memory use, application use and the network stack
- Network-based (NIDS)
- Monitors network traffic and analyses packets from different protocols to identify suspicious activity
- Placed at a viewpoint on a network to examine and analyse traffic
- Installed on a firewall or in a DMZ
- Installed behind a screened subnet
- May perform deeper analysis than many firewalls
- like stateful protocol analysis and deep packet inspection
Components of a IDS
- Sensors / Agents: collect and collate data from multiple viewpoints on a network
- Analysers: ascertain if an intrusion has taken place
- Reporting: notify the administrators via alerts on a console or graphical interface
Multiple sensors allow us to distribute capture, but centralise computing overhead
Detection Modes
- Stateful Protocol analysis
- More complex version of a stateful packet filter
- Hold detailed session information on protocols being used, examine for attacks
- Why is this user logging on as root?
- Why is this command being send a 1000 byte buffer as a parameter (buffer overflow)
- Computationally costly and requires the IDS have all possible versions of these protocols defined in its database
- Signature-based
- Fingerprinting sequences of operations or packets
- Like antivirus, signatures are created and stored in a database - operations as well as binaries
- If operations match a defined singature, then an alarm is triggered
- Include some form of attack language
- Mechanisms to describe sequences of events
- Maintain and monitor intermediate states and event transitions
- The pros and cons of these systems are identical to their anti-virus counterpart
- Computationally efficient
- Always spots know attacks
- Always misses unknown attacks
- Detailed signature databases must be kept up-to-date
- Example: If there is a large amount of
ICMPtraffic, manyTCPpackets (SYNpackets)- These connections going to a variety of other hosts
- If a host establishes more than 3 tcp connections to different hosts in 5 seconds, its port scanning
- Anomaly-based
- Built a model of normal and find deviations
- Anomaly detection has wide-ranging application from IDS to banking fraud
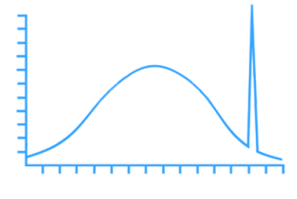
- Build up a picture of normal usage, and detect when usage moves beyond what is normal
- Always a trade off between false positives and false negatives
- Run a host within a quarantined environment and collect training data
- Constructed by monitoring audit logs
- Sometimes rely on analysis of sequences of system calls through normal behaviour
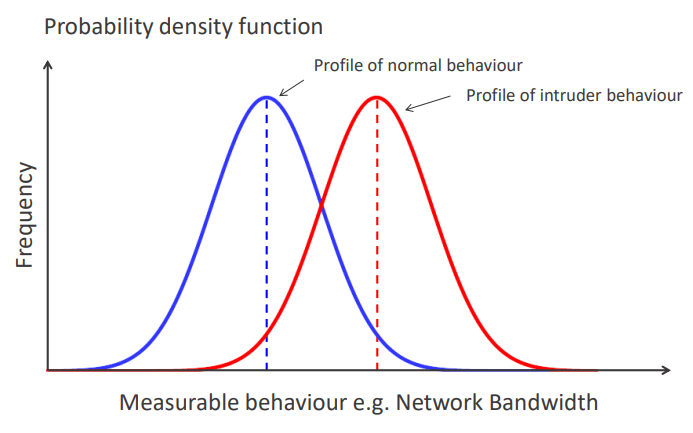
- However network traffic is more complex than a normal curve
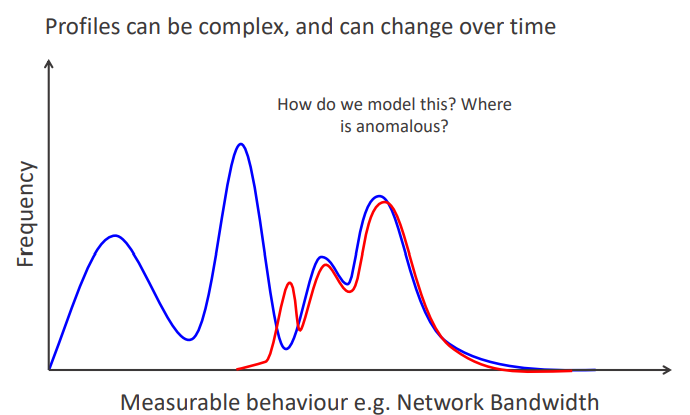
- Very hard to decide if network traffic is nefarious or not


Snort
- Snort is a powerful and well established IDS
- Also free!
- Uses rules to analyse network packets, and then can provide alerts or logging
- Snort has built in rules for detecting
nmapm a logged scan may look like this: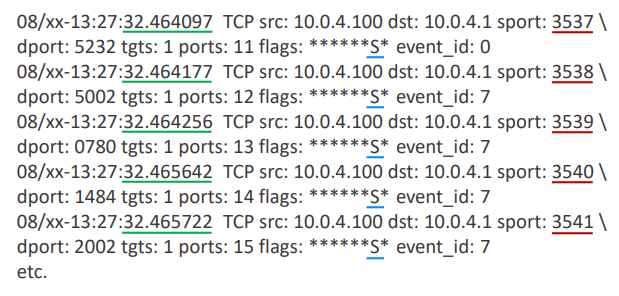
- The machine
10.0.4.1is sending out packets with incremented port numbers - The time stamps on the data show the packets are being sent extremely quickly
- All these packets are synchronised packets, its not waiting for
ACKpackets

Nmap Timings
- You can avoid detection when using
nmapby reducing the speed of the scan - The makes port scanning very hard to distinguish from general network noise
nmapcontains 6 timing options- paranoid mode leaves 5 minutes between packets
- insane mode is basically a DDOS attack
Machine Learning
- Machine learning approaches train a model to make predictions on data
- Support vector machines, neural networks etc
Neural Networks for ID
- A network can be pre-trained
- Sensor measurements are then passed through the network
- Activations in the specific output neuron signal an alert

- Scales badly
- Search space can increase exponentially
- Real-time data
- False negatives
- Limits in the representation
- What is normal can change
- Do we retrain and risk learning an intruders behaviour?